
Services · Cyber Security
Security operations, run as a service.
MSP Hub runs security for organizations that live on Microsoft. One team watches your identities, endpoints and tenants, contains what it finds, and shows you the evidence. Licensing for the security stack sits on the same MSP Hub agreement as the rest of your Microsoft spend.
What we watch
Most incidents start with a sign-in, not with malware. Watching the estate means watching three things at once.
Identities
Privileged role changes, risky sign-ins and policy drift across Microsoft Entra ID. Identity drift is caught when it starts, not at the quarterly review.
Endpoints
Every managed device runs our endpoint platform: detection and response, email security, DNS filtering and user awareness training, managed from one console at one per-user price.
Tenants
For organizations with more than one Microsoft tenant, coverage, policy and alerts roll up to one view, so nothing sits unwatched between tenants.
What happens when something fires
- 1
Notify
A person contacts your team with what fired, where, and what it touched.
- 2
Contain
The affected device or session is isolated while it is checked.
- 3
Close
Every event ends with a written record: what happened, what we did, and what changes.
Response targets are set in each agreement.
Built on the Microsoft security stack
We operate the security tools you already license before adding anything new: Microsoft Entra ID for identity and conditional access, Microsoft Intune for device policy and compliance, Microsoft Defender for endpoint and email threat protection, and Microsoft Sentinel where a full SIEM is warranted. Where a gap remains, our managed endpoint platform closes it. Everything lands on one MSP Hub agreement.
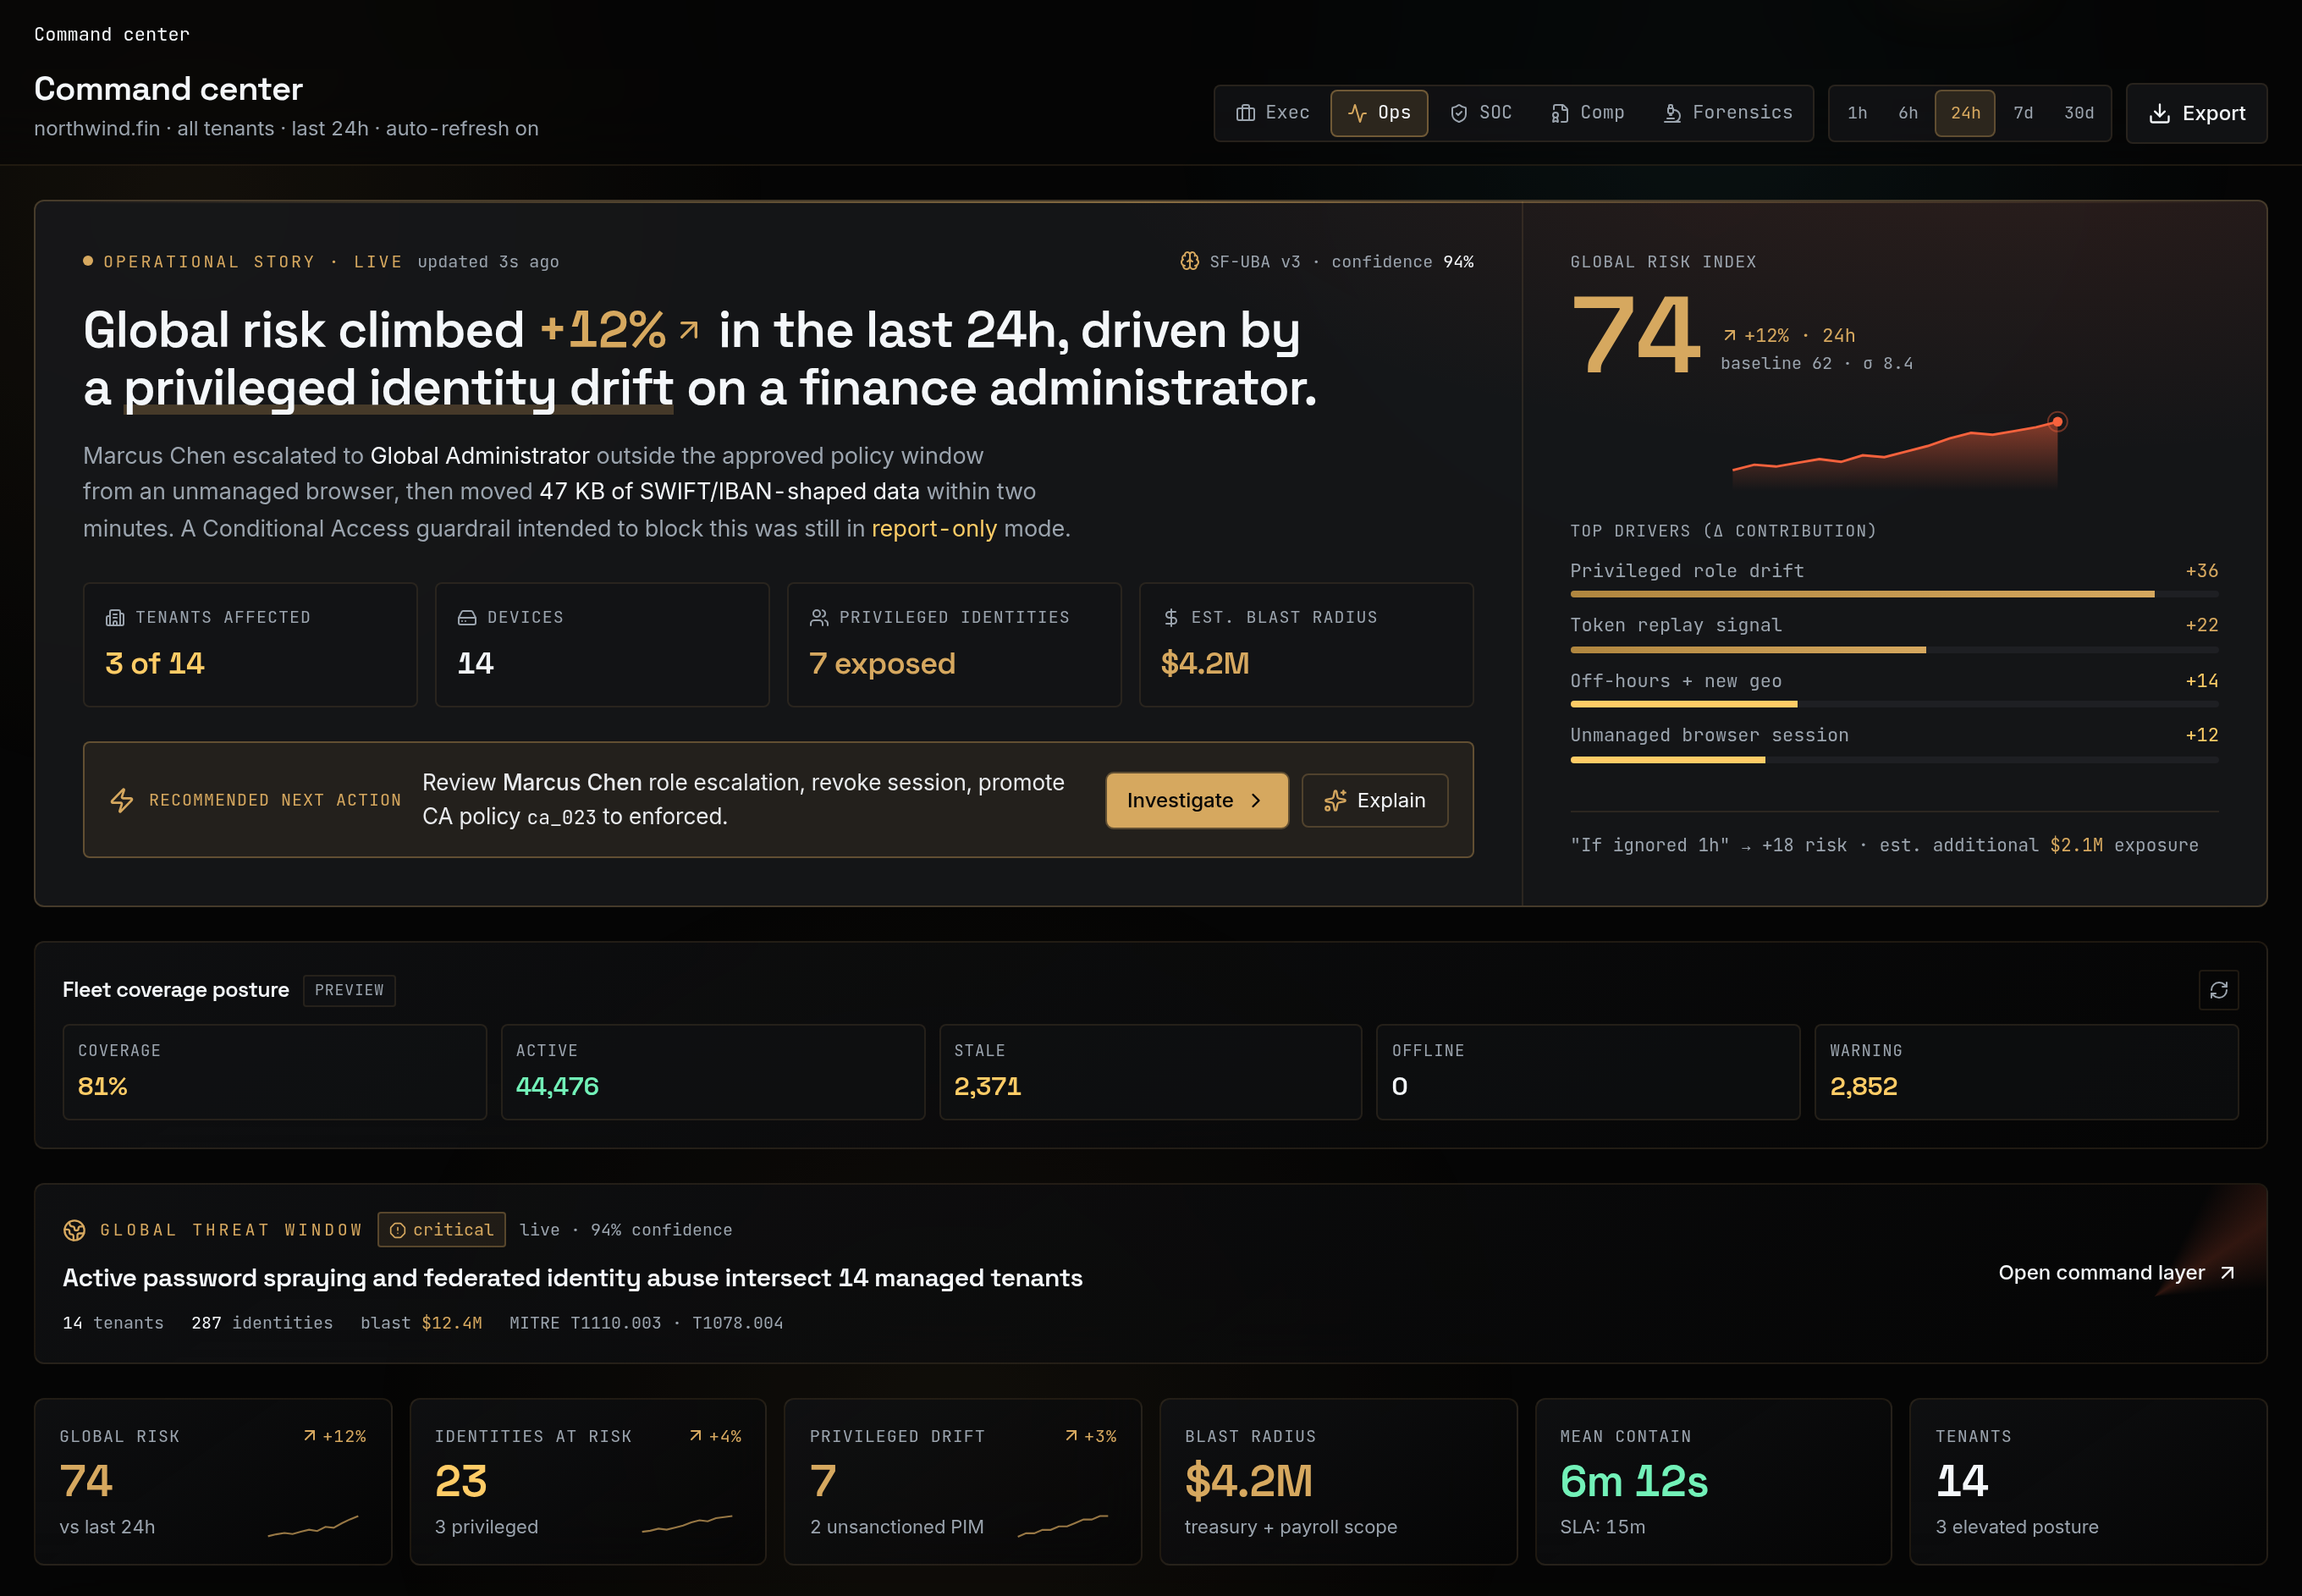
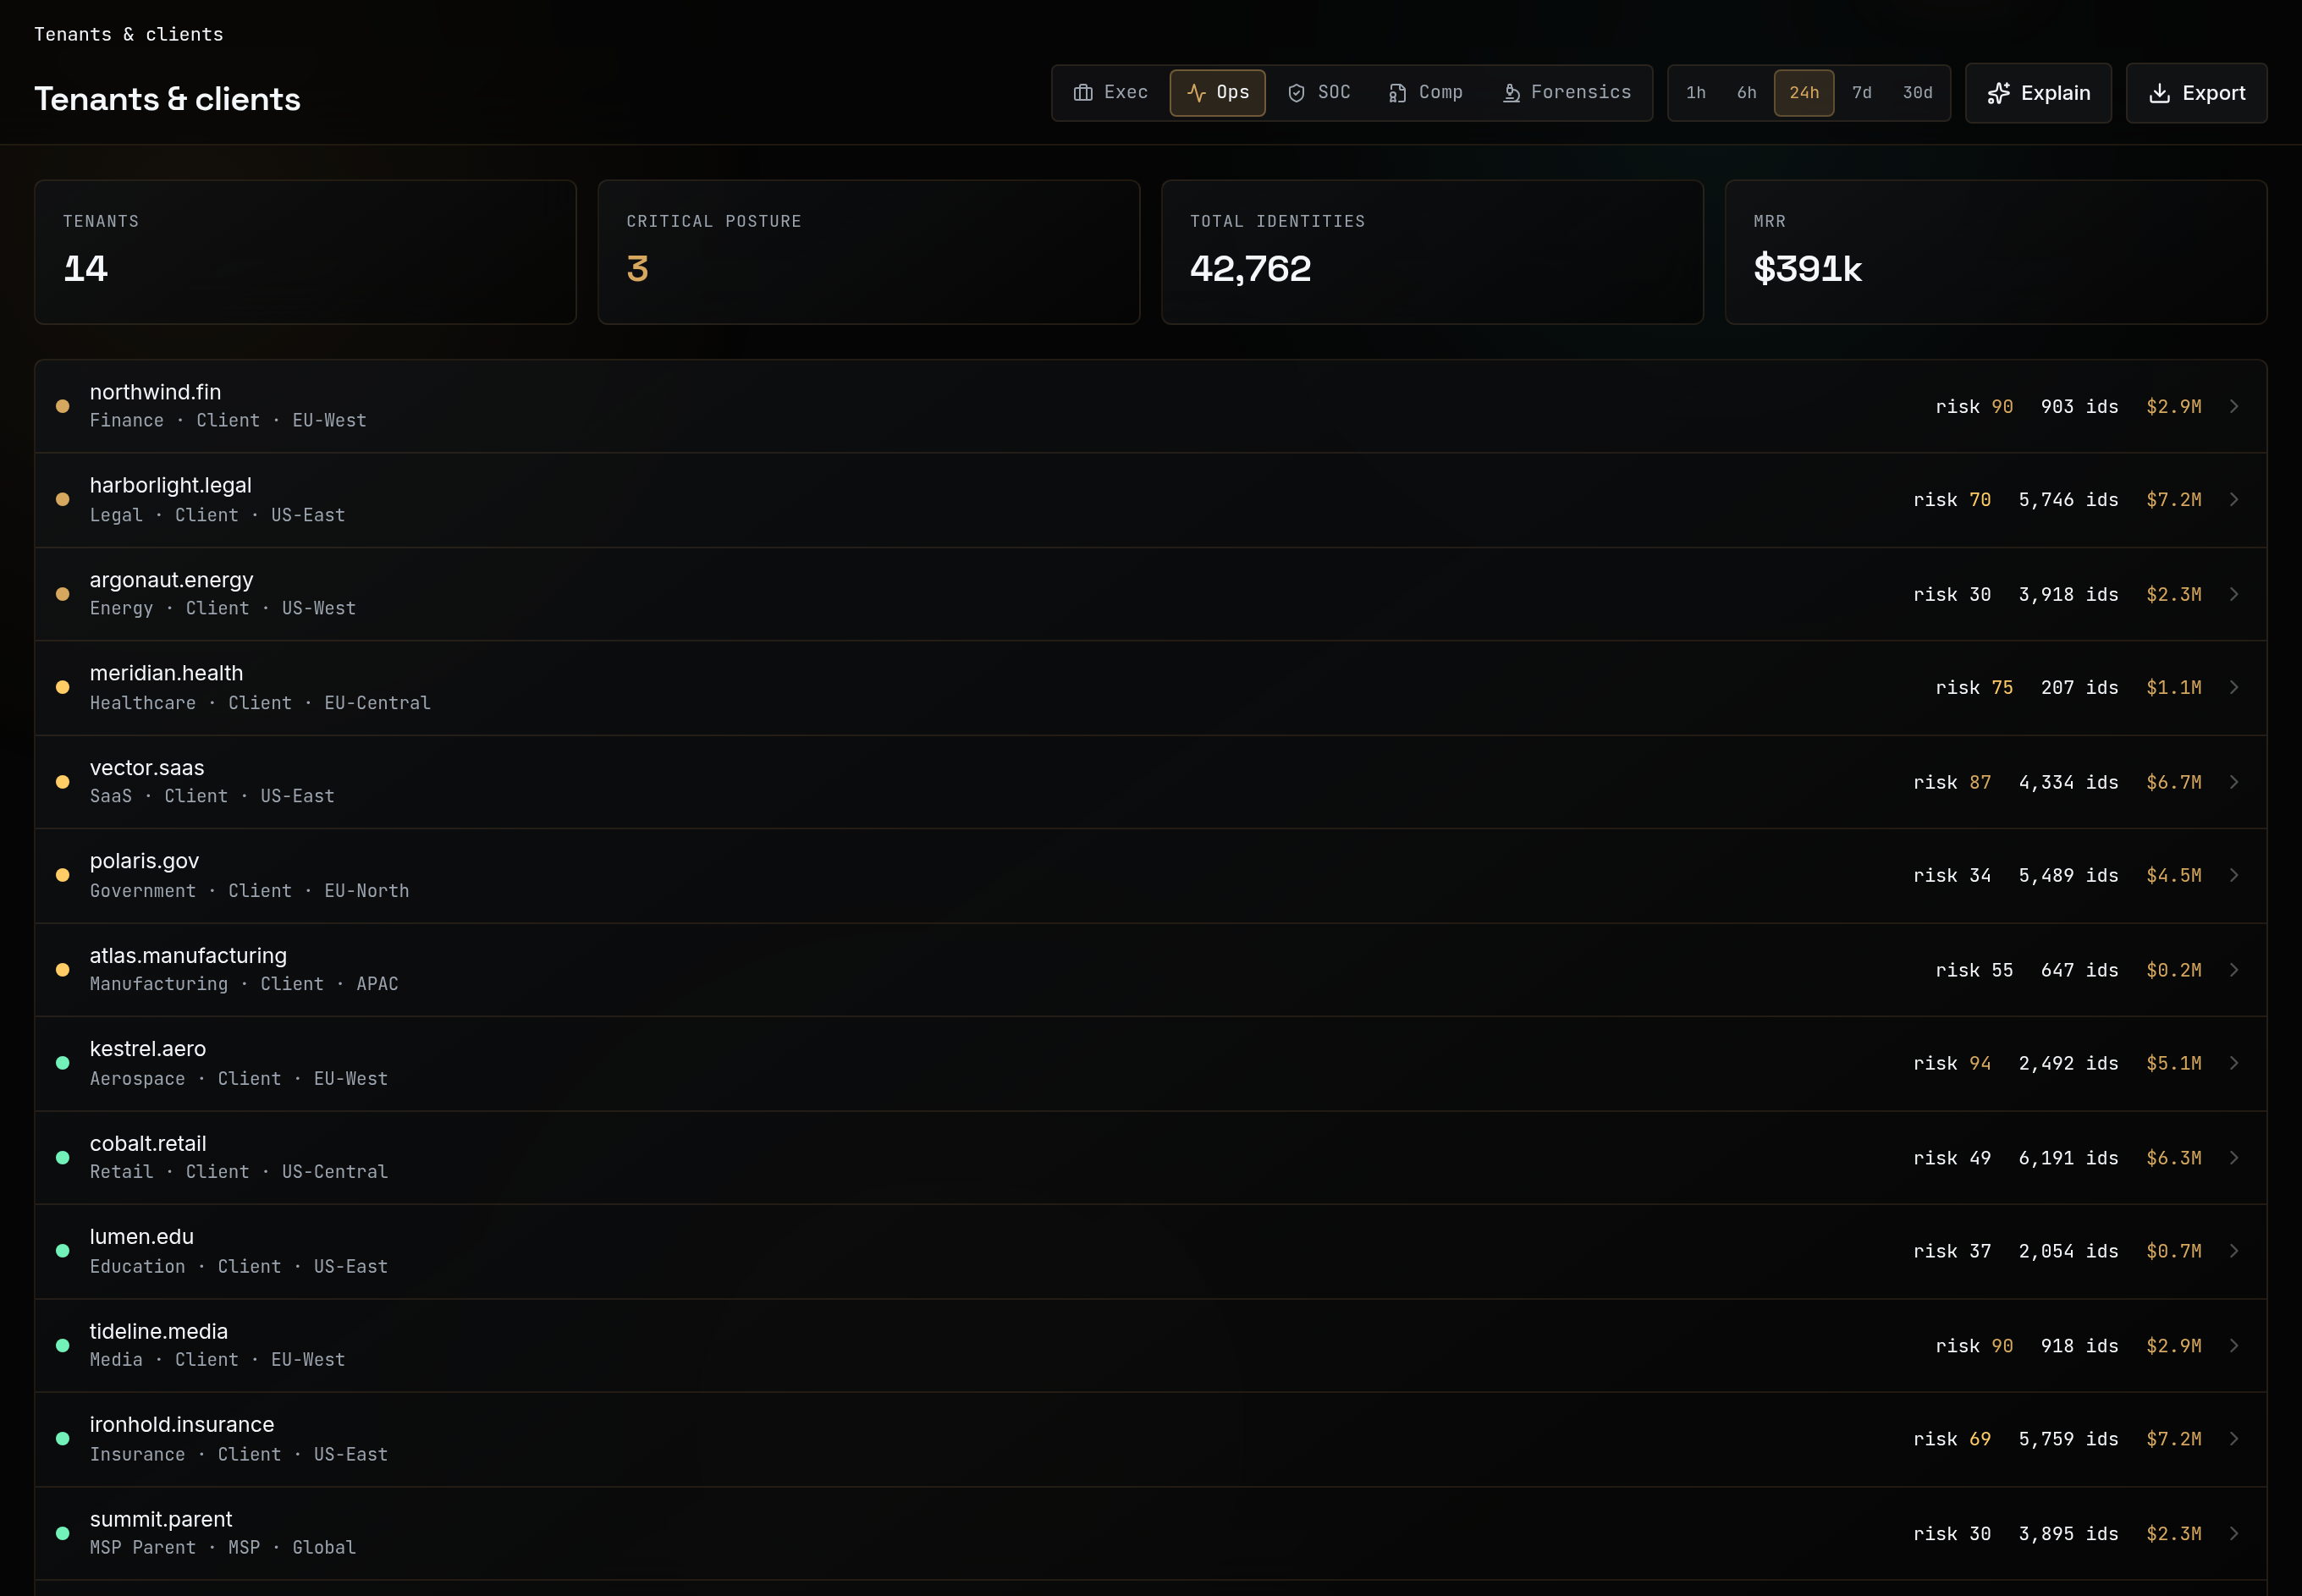
The console
One view of risk.
Our security console turns telemetry into an operational story: a global risk index, the drivers behind it, and the recommended next action — per tenant and across all of them.
How an engagement starts
- 1
Baseline
We read your estate: identity posture, device compliance, mail flow and current licensing.
- 2
Report
You get a written findings report and a fixed quote.
- 3
Run
We take the watch. Scope, pricing and terms are set in the agreement.
Next step