
HubX security
Who can see what, and how you can tell.
HubX signs users in through your identity provider, scopes access per organisation and per customer, records changes in audit logs, and reaches Microsoft tenants only through the CSP program's own mechanisms.
How access works
Four things to know before your security review.
01
Single sign-on with your identity provider
Microsoft Entra ID, Google or Okta through OpenID Connect, with managed domains routing each sign-in. Configured under Administration.
02
Users and roles at every level
Access is assigned per organisation and per customer. Dashboards, reports and HubAI are scoped to the billing subscription selected.
03
Audit logs
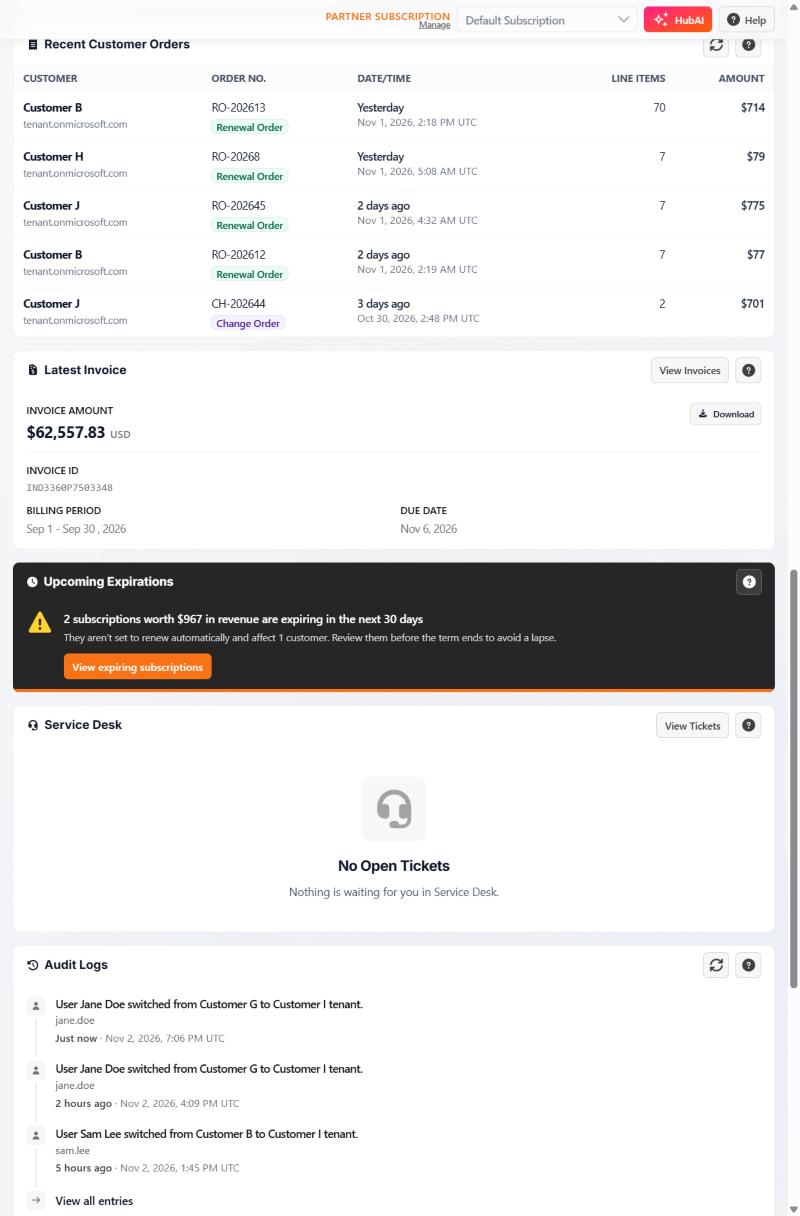
Organisation-wide and per customer, with the most recent events on the home page.
04
Microsoft access through Microsoft's mechanisms
Reseller relationships accepted by the customer, GDAP relationships with their status visible, and Microsoft Customer Agreement acceptance recorded per tenant.
In the product
The audit feed sits on the home page.
Recent account activity appears beside the latest invoice, upcoming expirations and Service Desk.
Certifications and agreements.
This page makes no certification or compliance claims. For questionnaires, data-processing terms or certification scope, ask the team directly.